


Active Distribution of Malicious HWP files Targeting CES 2020 Attendees
If you plan on signing up for the CES 2020 held in Las Vegas each year, watch out for the malicious file, disguised as a ‘CES 2020 entry form,’ that has been going viral.
On October 24, a malicious HWP file, named 'Application to Participate in CES 2020, USA,’ was reported to AhnLab Security Emergency-response Center (ASEC). HWP is a word processor program that is widely used in South Korea. ASEC has officially published information regarding this malicious file via its blog.
According to ASEC, an attacker used the CVE-2017-8291 vulnerability to insert malicious PostScript images into a normal HWP file to execute the malware.
<Summary of Sample>
- File Format: HWP (.hwp)
- MD5: f865ea5f29bac6fe7f1d976a36c79713
- SHA256: d4f055d170fd783ae4f010df64cfd18d8fa9a971378298eb6e863c60f57b93e3
- Attack Method: CVE-2017-8291 exploit
Malicious ShellCode is injected when the injected malicious PostScript runs the gswin32c.exe process or gbb.exe process and looks for any explorer.exe processes running. Most malicious activities take place in the explorer.exe process.
By inserting a malicious PostScript file, gswin32c.exe process or gbb.exe process runs to find a running explorer.exe process and injects the malicious ShellCode. As a result, malicious functions occur within the explorer.exe process.
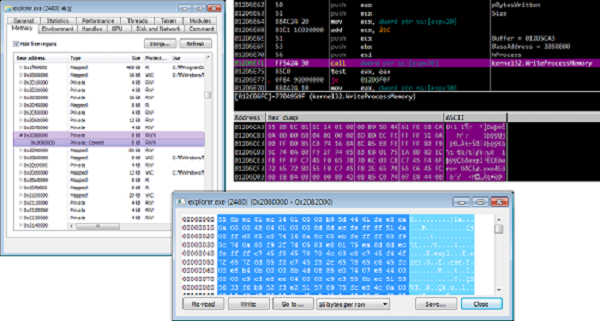
Figure 1. ShellCode injected in explorer.exe process
The injected ShellCode has the ability to search and verify a valid PE file by accessing a specific URL, as shown in Figure 2. ASEC has confirmed that the ShellCode communicates with the following four URLs:
- hxxps://thevagabondsatchel.com/wp-content/uploads/2019/09/public.avi - HTTP GET
- hxxps://www.juliesoskin.com/includes/common/list.php - HTTP POST
- hxxps://www.valentinsblog.de/wp-admin/includes/list.php - HTTP POST
- hxxps://www.necaled.com/modules/applet/list.php - HTTP POST
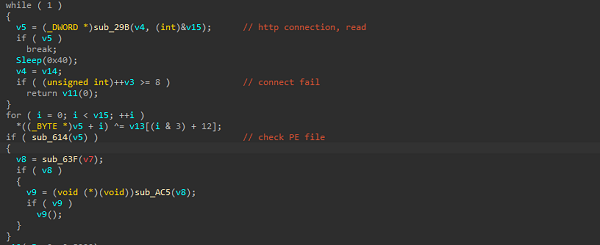
Figure 2. Checks PE file by accessing specific URL
The Consumer Electronics Show (CES) is the world's largest consumer electronics IT product showcase held in Las Vegas, US, every January. Cybersecurity threat malusing the event is expected to rise in number as the registration increases.
AhnLab’s V3 anti-malware solution detects the malware using the following alias:
<V3 Product Alias>
- HWP/Exploit (2019.10.24.05)
- Trojan/Win64.Hwdoor (2019.10.24.07)
- EPS/Exploit.S8 (2019.10.25.00)


