


Emotet Malware Returns! What is it after?
Recent analysis revealed that Emotet malware has come back to life and has resumed malspam operation using Word documents with malicious VBA Macro. It requires user interaction to download the malware and to ultimately infect the system; thereby users must be especially cautious.
ASEC (AhnLab Security Emergency-response Center) researchers have identified the spread of Word document with a malicious VBA Macro.
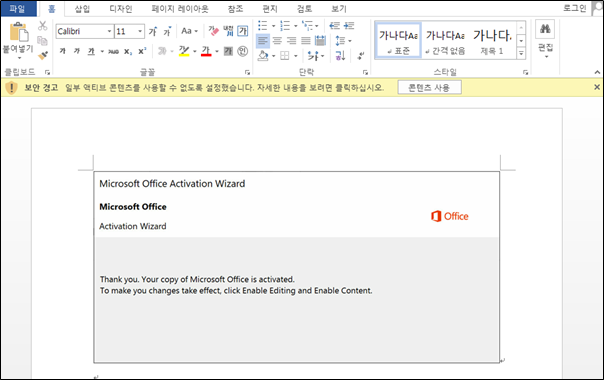
Figure 1. Word document with malicious VBA Macro
When the user opens the Word document, a message appears that lures the user to execute the VBA Macro, as shown in Figure 2. Malicious VBA Macro, executed by user interaction, initiates the PowerShell through WMI(Windows Management Instrumentation) and downloads the malware.
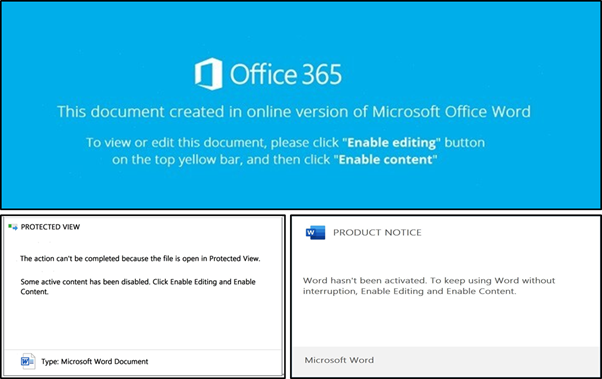
Figure 2. Message luring users to execute VBA Macro within the malicious Word document
Emotet is one of the most notorious botnet for providing Malware-as-a-Service(MaaS) to other cyber-criminal groups, such as Bitpaymer and Ryuk ransomware, allowing them to drop their malware alongside Emotet. Emotet is known to steal financial credentials. A major attack that took place late last year was to steal banking information using attached ‘invoice’ files. Emotet has gone silent for nearly four months since this May but has returned once again for full operation.
According to AhnLab’s recent analysis, VBA Macro spreading Emotet last November used CMD(Command) to execute the Powershell. However, recent attacks showed that VBA Macro uses WMI to execute PowerShell. When the PowerShell initiates via WMI, a URL among the five URLs set-up by the attacker is connected to download and runs the malware.
Emotet malware encrypts credentials, such as Window version of the infected PC, CPU architecture, CRC(Cyclic redundancy check) of the malicious file, and Session ID of PEB, with the information of the processes running on the PC and delivers it to the attacker’s server.
Also, recent Emotet has been identified to create and delete file names using a specific algorithm. This kind of activity can be seen to remove existing malware and download new ones.
AhnLab’s anti-malware solution, V3 detects and blocks Emotet malware by preventing the PowerShell from downloading it and shows an alert when doing so. V3 uses behavioral-based and generic technology to detect Emotet-related malware using the following alias.
<V3 Product Alias>
- Malware/MDP.Download.M1197
- Malware/MDP.Emotet.M2077
- VBA/Downloader.S55
Therefore, it is required that all anti-malware solutions, such as V3 engine, be up-to-date and real-time detection functions fully initiated. Macro within the Word document can start the infection. Thereby users must be extra careful when using Macro in unreliable Word documents.


