


New Ransomware Disguised as a Utility: Dharma Ransomware
A new variant of Dharma ransomware, which is disguised as a file management utility, was discovered.
This ransomware is disguised as a BulkFileChanger, a file management utility that allows users to easily change file attributes. It is difficult to distinguish between the real utility and the ransomware disguised as the utility because they have the same file icon and properties.
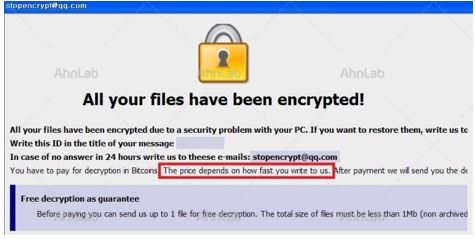
Dharma ransomware displays a ransom note on the screen once encryption is complete. Unlike the previously found Dharma ransomware that specified the bitcoin amount in the ransom note, this variant urges users to send an email to negotiate the price.
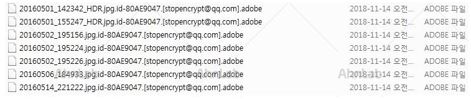
As shown in Figure 2, the ransomware encrypts the file and appends .adobe to the file extension.
Dharma ransomware often spreads through Remote Desktop Protocol (RDP) so users must be aware of their RDP security. Some common methods for RDP security are as follows.
1. RDP access control: Only allow access to authorized users
2. Password management: Use complex passwords and change them periodically
3. Change and manage the RDP default port (3389)
4. Apply Windows security updates and keep vaccine programs up-to-date
The alias identified by AhnLab's anti-malware solution, AhnLab V3, is as below:
- Trojan/Win32.Inject


