


Malware in Full Swing Ahead of the PyeongChang Olympics
As we near the opening of the PyeongChang 2018 Olympic Winter Games, more malware that impersonates Winter Games authorities and websites are being found. Users are warned to be on extra alert as one of the discovered malware programs mentioning 2018 Olympic Winter Games.
A particular malware, OlympicGame.exe, pretends to be the Winter Olympic Games by using the Olympic symbol as the file icon as shown in Figure 1.
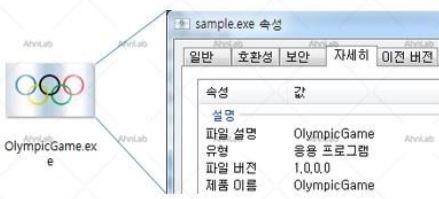
[Figure 1] Malware disguised as the Olympics symbol
If the executable file is executed, a fake Olympics lottery registration form is displayed with fields for inputting the user’s name and email address as shown in Figure 2. However, most unsuspecting user fails to notice that the emblem used for the file icon is not the official emblem of the PyeongChang Winter Olympic Games.
Thus users input their personal information–name and email–and click on the Register button, which then sends the information to the attacker.
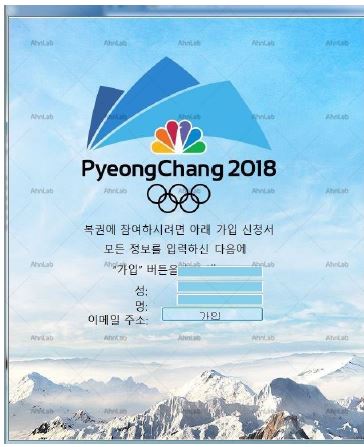
[Figure 2] OlympicGame.exe asking for user’s information
However, that is not the end. It also conducts malicious activities within the user's computer. It creates a winupdate.exe file within a temporary path when the malware is executed, and this file then registers malware in the startup program or schedules it as a job for automatic execution. Furthermore, it downloads additional malware via the C&C server.
Another malware disguised as a document related to the PyeongChang Winter Olympics has been found. The file was designed to look like it originated from the Ministry of Agriculture, Food and Rural Affairs (MAFRA) to convey information to relevant institutions in preparation for the Winter Olympics. However, the file neither was prepared by MAFRA nor does it contain relevant information.
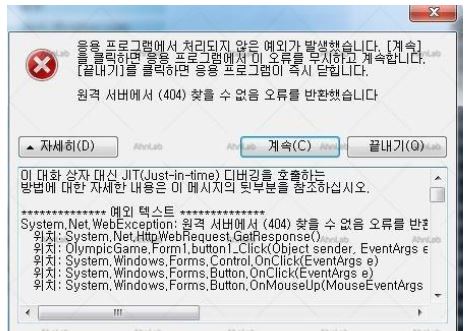
[Figure 3] Security warning when opening the document
When this DOC document is opened, a yellow message bar appears on top to inform the user that file macros have been disabled, as shown in Figure 4. Normally, macros increase the efficiency of completing tasks within the document, but malicious macros replace regular tasks with malware without the user's knowledge.
Thus, to induce users to enable macros by clicking [Enable Contents], and once the macro function is enabled, the malicious code is executed.
The malicious macro code embedded in the DOC file executes the PowerShell code. The executed PowerShell code accesses the designated URL to download an additional file.
Judging by the effort to disguise the file as an official government document, this malware can be seen as targeting South Korean organizations involved with the PyeongChang Olympics.
As these types of malicious files use email attachments for their distribution, users are warned to take extra precautions when downloading attachments by checking the sender’s credentials and avoiding downloading attachments from unidentified senders. Also, if a warning message appears to enable macros in an attachment, it is recommended that you do not enable macros right away but use an antivirus to scan the file or withhold from enabling it.
The number of more sophisticated malware designed to target the PyeongChang Winter Olympics is rising as we near the start of Olympic Games. Due to the global size of the event and the high potential damage, it seems likely that the attackers will take their efforts further. Users are warned to be mindful of these attacks.


