


Kraken Cryptor, the Cruel Destroyer
A new variant of the Kraken Cryptor was found recently being distributed through online advertisements. The variant operates by encrypting the files on the infected system and deleting the traces of original files left on the system. This results in greater difficulties for decrypting the files and the potential damage to the system is likely to be high.
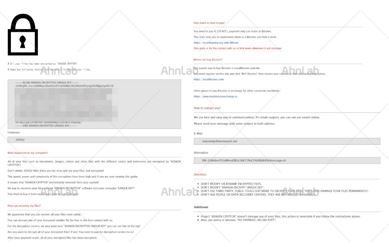
[Figure 1] Kraken Cryptor v1.6 Ransom Note
Kraken Cryptor is a ransomware that named itself after the kraken, a legendary monster from Norse mythology which also famously appeared in the movie, Pirates of the Caribbean. Kraken Cryptor began to attract wide attention in August 2018 with the release of version 1.2, which uses the Fallout Exploit Kit.
The Fallout Exploit Kit is a relatively new attack tool that distributes ransomware using a malvertising technique that exploits online advertising. It is known to have been used to spread various malware including GandCrab ransomware, SmokeLoader, and a mining malware from late July to late August of 2018. The attacks were discovered in South Korea, Japan, Southern Europe, and the Middle East.
The Fallout Exploit Kit first checks the browser of a user PC. Only when the PC meets certain conditions will the kit infect the PC with malware, such as ransomware, by using malvertising methods. However, a new attack method was discovered in September, where Kraken Cryptor attacked a specific website and replaced the normal installation files with malicious file.
The latest variant, Kraken Cryptor version 1.6, uses a new distribution method using malicious advertisement banners on websites, such as Torrents and adult websites. When a user accesses a website containing this advertisement, the ransomware checks the user's PC environment using the Fallout Exploit Kit. When the PC meets certain conditions, the user is redirected to a specific page and infected with ransomware.
Once Kraken Cryptor v1.6 has infiltrated the user's PC, it creates a file entitled krakentemp0000.exe in the% Temp% folder, and attempts to bypass the User Account Control (UAC) of Windows. This is intended to prevent a notification window from appearing and asking the user for confirmation when launching the ransomware.
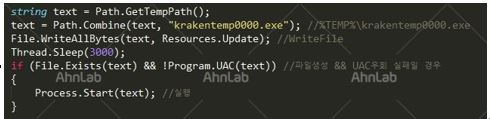
[Figure 2] Main Codes of Kraken Cryptor v1.6
The %Temp%\krakentemp0000.exe file installed by Kraken Cryptor in a specific location bypasses UAC and executes malware by exploiting a vulnerability of an Event Viewer (eventvwr.exe), a program in the Windows operating system. However, UAC bypass does not occur for Windows 10 or later, as this vulnerability has been patched.
Upon execution, the Kraken Cryptor not only encrypts the files on the infected PC but downloads a non-malicious file deletion program to remove all traces of original files from the infected system drive. This is to prevent users from recovering original files using file recovery programs.
As shown in [Figure 3], Kraken Cryptor changes the file extension name to a 5-digit string of random characters during encryption. Once encryption is complete, it also creates a ransom note file called # How to Decrypt Files-[Encryption Extension].html.
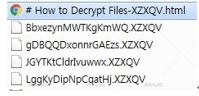
[Figure 3] Encrypted Files and Ransom Note File
The aliases identified by AhnLab's anti-malware solution AhnLab V3 are as below:
<V3 Product Alias>
Trojan/Win32.Ransom
Malware/Win32.Generic
We recommend you to take extra caution to avoid infection from the Kraken Cryptor malware as files on the system will be lost beyond recovery. To prevent such damage, you should keep from using unsafe websites and back up important files to a separate device. In addition, it is important to apply the latest security patches to the operating system and major programs, as Kraken Cryptor checks for a vulnerable PC environment before infection.


