95% Detections! MITRE ATT&CK Evaluation Round 6
MITRE ATT&CK Evaluations, just completing its sixth round, is recognized worldwide as one of the most trusted security product tests, considering its similarity to real-world threats and completeness of attack scenarios. A total of 19 cybersecurity companies participated in round 6. AhnLab was the only South Korean company to have taken part in the evaluation for four consecutive rounds since round 3.
In round 6, MITRE tested participants on their ability to detect and respond to the real-world techniques and tactics of multiple threat actors. This methodology contrasts with previous rounds, which focused on emulating the adversary behaviors of a single threat group.
The detection capability of AhnLab EDR, AhnLab EPP, and AhnLab XDR was rigorously assessed, and our products achieved 95% detections for malicious ransomware behaviors of CL0P and LockBit that the MITRE team emulated.
Ransomware (CL0P and LockBit)
Enterprise Round 6 focused on LockBit and CL0P to emulate common behaviors prevalent across the ransomware ecosystem. LockBit, which law enforcement agencies have described as the “most deployed ransomware variant across the world,” is known for its use of sophisticated tools and dual targeting of Windows and Linux systems. CL0P is a ransomware family associated with the TA505 criminal group and leverages the “steal, encrypt, and leak” strategy across a variety of regions and sectors.
The result verified our advanced detection and analysis of real-world threats
Enterprise Round 6 focused on LockBit and CL0P to emulate common behaviors prevalent across the ransomware ecosystem. LockBit, which law enforcement agencies have described as the “most deployed ransomware variant across the world,” is known for its use of sophisticated tools and dual targeting of Windows and Linux systems. CL0P is a ransomware family associated with the TA505 criminal group and leverages the “steal, encrypt, and leak” strategy across a variety of regions and sectors.
We were able to secure 95% visibility by detecting 56 out of 59 substeps in Ransomware scenarios across Windows and Linux platforms. Our products provided high-quality evidence with comprehensive and contextual analysis into emulated threat behaviors. Also, the chart below indicates that our detection results and capabilities are competent among our industry peers.
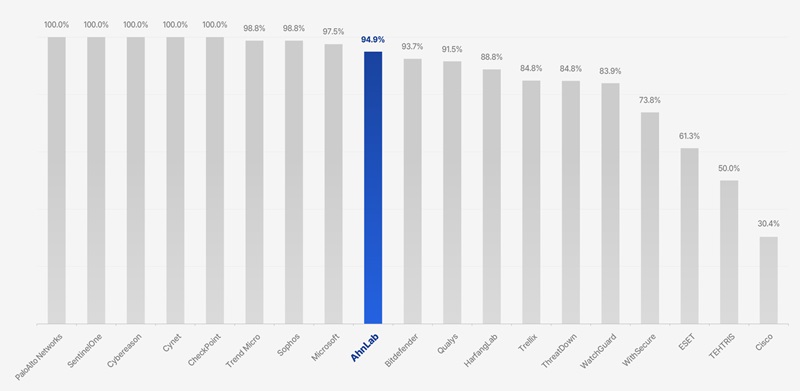
Figure. The “Detections” results of participants in Round 6
*The results in the figure were analyzed by AhnLab. MITRE does not rank its evaluation participants.
On top of that, our products delivered 49 “Techniques” among 56 substeps detected. This demonstrates that our customers can thoroughly understand the underlying context (how and why) of malicious behaviors and make informed decisions by referring to the evidence of our solutions. The result is even more meaningful as context-aware detection is key to triggering an optimal response, especially when we have to deal with sophisticated and ever-evolving modern cyber threats.
Please refer to the eBook to learn more about our results of MITRE ATT&CK Evaluations Round 6
- AhnLab


