


Makop Ransomware Distributed via Copyright Infringement Notice Emails
The ASEC analysis team has introduced the distribution of Makop ransomware disguised as job applications in its previous blog posts. This week, the team confirmed that the ransomware is being distributed via copyright infringement notice emails. Let's see how the attack methods have changed apart from the subject of the email attachments.
< To read the full analysis regarding Makop ransomware's recent distribution, visit ASEC Blog. >
Unlike the last time, the compressed file is attached with the .dat extension instead of .zip and to avoid the e-mail attachment scan. The file attachment was locked with passwords, which turned out to be the the date the mail distribution.
Inside the attached file, there is a file compressed with Alzip which contains three files as shown below.
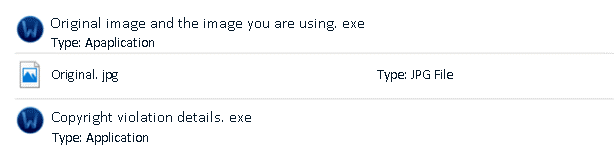
Figure 1. Files inside the email attachment
Among them, the image named original.jpg file is a normal executable file, and the other two are the ransomware. The two malicious files have disguised themselves as CCleaner Installer, as shown in Figure 2.
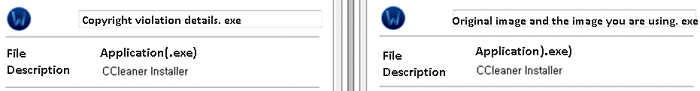
Figure 2. Properties of files
This ransomware has been continually distributed as fake job applications and materials related to copyright infringement.
As such, users are advised to take extreme precaution when opening emails related to this topic and refrain from opening files attachments sent by an unknown user.
AhnLab’s anti-malware software, V3, detects and blocks the malware using the aliases below.
[File Detection]
Ransomware/Win.MakopRansom.C4439397
[Behavior Detection]
Malware/MDP.Behavior.M3635
[IOC Info]
237d76f961f8f550c4c4bbfab30153a6
< To read the full analysis regarding Makop ransomware's recent distribution, visit ASEC Blog. >


