


Do Not Get Lost in the Maze of Ransomware
Maze Ransomware, which exploits vulnerabilities in Internet Explorer (IE), has emerged in the wake of another series of new Ransomware.
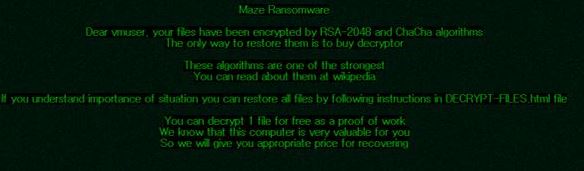
[Figure 1] Ransom note of Maze Ransomware
Maze Ransomware has been found to be spreading using the Fallout Exploit kit, a malware generator, and a frequently visited vulnerable web browser. Maze Ransomware encrypts the infected PC's files and changes the extension to random multiple strings. Also, to inform the user of the infection, they create the file DECRYPT-FILES.html as shown in Figure 2 and change the background as Figure 1.
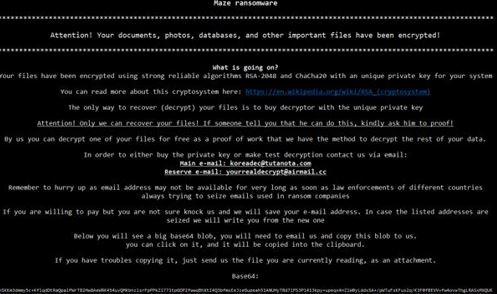
[Figure 2] Html file created by Maze Ransomware
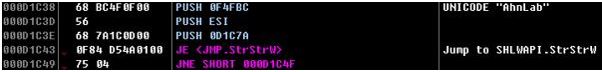
On the other hand, this Ransomware has been confirmed that if the PC has a folder named "AhnLab", internal files of the folder are excluded from encryption. It is aimed at bypassing the security solution of AhnLab installed in user PC such as V3.
AhnLab’s V3 products detect the ransomware under the following aliases:
<V3 Product Aliases>
- Trojan / Win32.RansomCrypt (2019.05.28.06)
- Malware / MDP.Ransom.M1171


