


STOP Ransomware Stealing Information was Discovered
Ransomware is continuing to evolve. Now, ransomware is largely changing from file encryption and money demands based programs to stealing information from infected PCs. Recently a ransomware named STOP was discovered that not only steals the information of the infected PC, but even the personal information of the user and their private key for cryptocurrency.
This STOP ransomware infects the PC, encrypts the files, and demands cryptocurrency for the decryption of the files. On top of that, it downloads additional malicious files including AZORult, which is a malware that steals personal information.
The "updatewin.exe" file is another additionally downloaded file. Once downloaded, this file displays a notification window that is almost identical to the genuine Windows Update window as shown in Figure 1. This tricks the user into believing that a Windows update is in progress. However, it conducts malicious actions by displaying the message "Do not turn off your computer" for the update while, in fact, it is encrypting the files in the computer and stealing information.
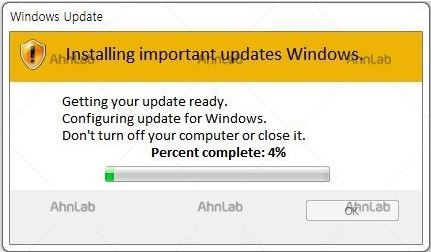
[Figure 1] Malware Disguised as the Windows Update Window
And AZORult malware steals personal information such as the OS information of the infected system, the password stored in PC, Skype conversations, the private key information of cryptocurrencies, and sends it to the attacker. In order to conduct this malicious act, AZORult excludes these kinds of files containing personal information from the target of encryption.
So, STOP ransomware is a new type of ransomware which distracts the user using a Windows lookalike program as seen in Figure 1 to secretly steal personal information, encrypt other files on the PC, and append .PROMORAD to the encrypted file names. It also shows a ransom note like in Figure 2 shown below to inform the user of the infection and demands money in exchange for the decryption of files.
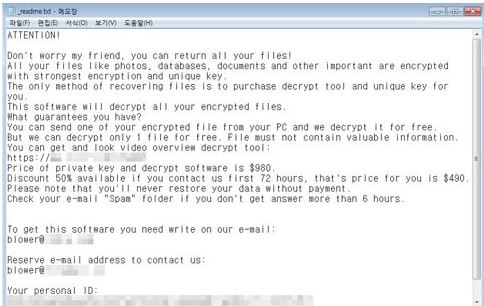
[Figure 2] STOP Ransomware’s Ransom Note
AhnLab’s V3 products detect STOP ransomware under the following alias:
<V3 Product Alias>
- Malware/Win32.Ransom
- Malware/Win32.Generic
- Trojan/Win32.Generic
- Win-Trojan/Gandcrab10.Exp
- Win-Trojan/Gandcrab10.Exp


