The Malware Disguised as a Flash Player Update
A new malware is being distributed disguised as an Adobe Flash Player update file. The malware is designed for mining cryptocurrencies but can also download additional malware designed for other types of attacks, such as DDoS attacks.
The malware induces user to access to a fake website and then displays a fake Flash Player update message in Portuguese, as shown in Figure 1. The fake update message looks almost identical to a real update message.
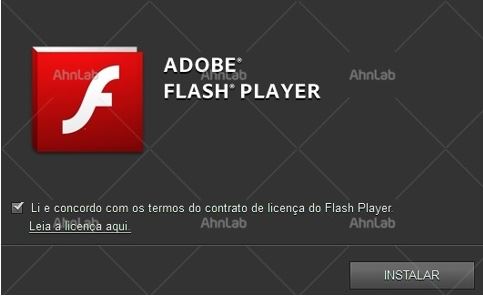
[Figure 1] Fake Adobe Flash Player Update Screen
Once a user clicks the installation button, a malicious file Flash-2018.exe will be downloaded. The file is executed and the user’s computer connects to the attacker's C&C server to download additional malicious files.
These other files are bots with malicious intents that steal information of the infected PC and execute commands received from the C&C server. The code of the bot includes a text string, "Rarog," as shown in Figure 2.
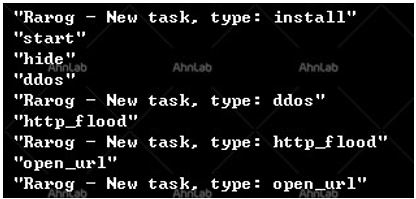
[Figure 2] Rarog String in Bot Malware Code
Rarog is a malware that was first discovered in June 2017 and was known to be a malware for mining cryptocurrency. However, Rarog is in fact a malware bot that carries out other forms of attacks, such as DDoS attacks or downloading additional malware. The creator of Rarog sells this malicious code in underground forums and even operates a page to manage the worldwide infections, as shown in Figure 3.
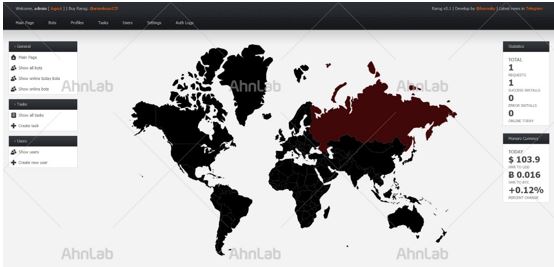
[Figure 3] Rarog Administrator Page
The Rarog malware discovered this time tries to communicate with a designated domain (rarogvip[.]ru) and sends the collected information to the administrator page. It also downloads additional cryptocurrency mining malware, Miner, from the C&C server and mines cryptocurrency without the user knowing.
The mined cryptocurrency is sent to a repository, such as Bitbucket, as shown in Figure 4. This repository is presumably owned by the attacker and contains additional malware that can be downloaded.
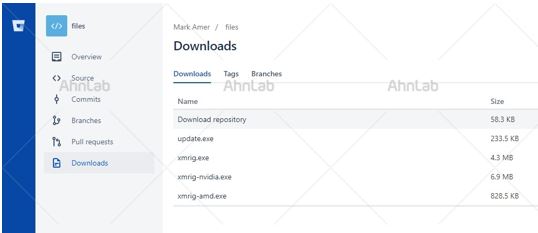
[Figure 4] Bitbucket Repository of the Rarog Creator
The aliases identified by AhnLab's anti-malware solution, AhnLab V3, are as below:
<V3 Product Alias>
- Malware/Gen.Gen eric
- Trojan/Win64.Miner
- Unwanted/Win32.BitMiner
- Unwanted/Win64.XMR-Miner


